How DNS Resolution Works: A Practical Guide
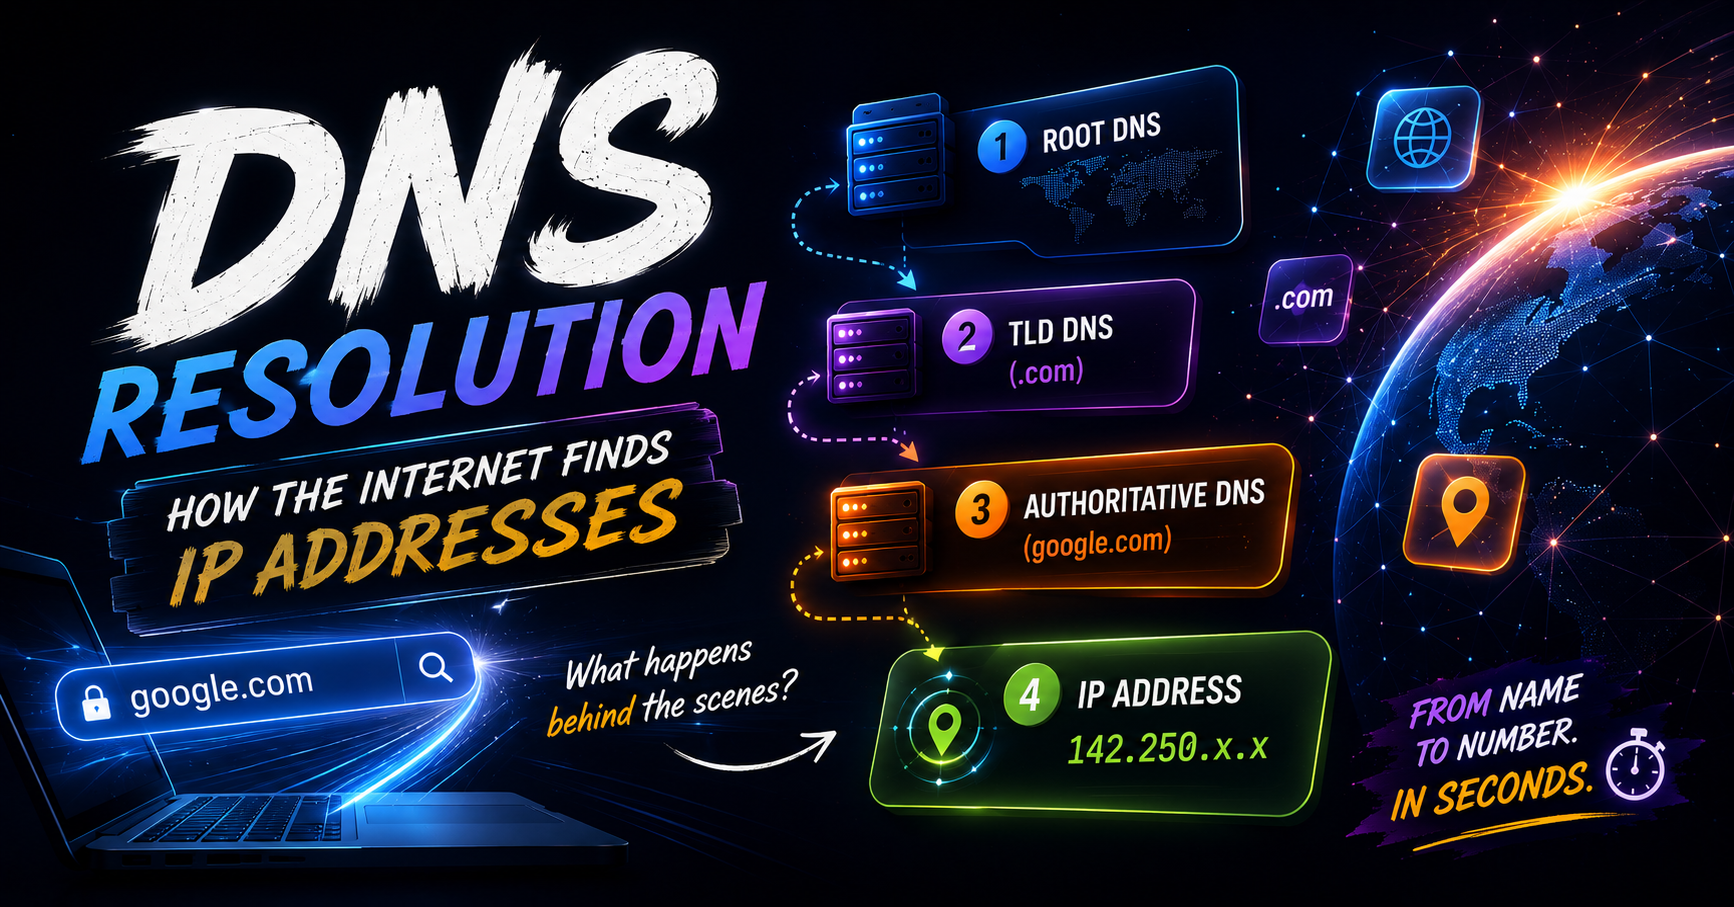
You type google.com into your browser, press Enter, and the website appears.
But computers do not naturally communicate using names like google.com. They communicate using IP addresses such as 142.250.x.x.
So how does your computer find the IP address behind a domain name?
This is where DNS (Domain Name System) comes in.
Think of DNS as the internet's phonebook. It translates human-readable domain names into IP addresses that computers can use to communicate.
In this article, we'll understand how DNS resolution works from the root DNS servers all the way to the authoritative name servers, using the dig command to inspect each step.
What Is DNS Resolution?
DNS resolution is the process of finding the IP address associated with a domain name.
For example:
google.com
    ↓
DNS Resolution
    ↓
IP Address
    ↓
Browser connects to the server
The interesting part is that DNS is organized as a hierarchy.
A simplified DNS hierarchy looks like this:
                    Root (.)
                      |
                    .com
                      |
                 google.com
                      |
             Authoritative DNS
                      |
                IP Address
The three important levels are:
Root DNS servers
TLD name servers
Authoritative name servers
Before looking at each one, let's understand the tool we'll use.
What Is dig?
dig stands for Domain Information Groper.
It is a command-line tool used to inspect DNS information and troubleshoot DNS problems.
For example:
dig google.com
It can show information such as:
DNS records
IP addresses
Name servers
Query status
Response time
Which server answered the query
Instead of simply asking, "What IP address does this domain have?", dig lets us look deeper into how DNS works.
1. dig . NS — Finding Root Name Servers
Start with:
dig . NS
Here, . represents the DNS root.
The NS means Name Server.
An NS record tells us which DNS servers are responsible for a particular DNS zone.
So:
dig . NS
asks:
"Which name servers are responsible for the root DNS zone?"
The response contains root name servers such as:
a.root-servers.net
b.root-servers.net
...
These are operated by different organizations around the world.
The root servers do not normally tell you the IP address of google.com.
Instead, they know where to find the next level: the TLD name servers.
2. dig com NS — Finding TLD Name Servers
Next:
dig com NS
Here, com represents the .com Top-Level Domain (TLD).
This asks:
"Which name servers are responsible for the
.comdomain?"
The response provides name servers responsible for the .com TLD.
These are called TLD name servers.
Their job is not to know every domain's IP address. Instead, they know which authoritative name servers are responsible for individual domains under .com.
For example:
Root DNS
    |
    | Where is .com?
    ↓
.com TLD Servers
    |
    | Where is google.com?
    ↓
Google's Authoritative DNS
This hierarchical design allows DNS to scale to billions of domain names.
3. dig google.com NS — Finding Authoritative Name Servers
Now run:
dig google.com NS
This asks:
"Which name servers are authoritative for
google.com?"
The response contains the authoritative name servers for the domain.
An authoritative DNS server is the server that has the official DNS information for a domain.
It can contain records such as:
A— IPv4 addressAAAA— IPv6 addressMX— Mail serverCNAME— AliasNS— Name serverTXT— Text information
The important idea is:
Authoritative DNS servers are the source of truth for a DNS zone.
For google.com, its authoritative DNS infrastructure can provide the DNS records needed to resolve the domain.
4. dig google.com — Getting the IP Address
Now run:
dig google.com
This performs a DNS lookup for google.com.
The response commonly contains an A record, which maps the domain to an IPv4 address.
You may see something like:
google.com. 300 IN A 142.250.x.x
The important parts are:
google.com — domain name
300 — TTL (how long the response can be cached)
A — IPv4 address record
142.250.x.x — returned IP address
Your actual IP may differ because large services can use multiple addresses and DNS-based traffic distribution.
What Happens During Real DNS Resolution?
When you enter:
https://google.com
your computer usually does not start by contacting a root server every time.
Instead, the request commonly goes through a recursive DNS resolver.
This resolver may be provided by your ISP, organization, router, or a public DNS service.
A simplified resolution flow looks like this:
Browser
   |
   | "What is the IP of google.com?"
   ↓
Recursive DNS Resolver
   |
   | 1. Ask Root
   ↓
Root DNS Servers
   |
   | "Ask the .com TLD servers"
   ↓
.com TLD Servers
   |
   | "Ask google.com's authoritative servers"
   ↓
Authoritative DNS Servers
   |
   | "Here is the DNS record"
   ↓
Recursive Resolver
   |
   | IP address
   ↓
Browser
The resolver performs the work on behalf of your computer.
Why Does the Resolver Matter?
The recursive resolver can cache DNS responses.
For example, if another user recently requested google.com, the resolver may already have its answer stored.
Then instead of repeating:
Root → TLD → Authoritative
it can return the cached result immediately, as long as the record's TTL (Time To Live) has not expired.
This makes DNS resolution faster and reduces unnecessary traffic to higher-level DNS servers.
Connecting dig to the Real World
The commands we used represent different parts of the DNS hierarchy:
dig . NS
     ↓
Root DNS Servers

dig com NS
     ↓
.com TLD Name Servers

dig google.com NS
     ↓
Authoritative Name Servers

dig google.com
     ↓
DNS Record / IP Address
In a real browser request, these steps happen behind the scenes through a recursive resolver.
Once the browser receives the IP address, DNS has done its job.
The browser can then connect to that server using protocols such as TCP/IP and HTTP/HTTPS.
Final Mental Model
DNS is not one giant server containing every domain and IP address.
It is a distributed and hierarchical system.
Remember the flow:
Domain Name
     ↓
Recursive Resolver
     ↓
Root DNS
     ↓
TLD DNS
     ↓
Authoritative DNS
     ↓
DNS Record
     ↓
IP Address
And remember what each level does:
Root DNS: Points toward the correct TLD servers.
TLD DNS: Points toward the domain's authoritative name servers.
Authoritative DNS: Provides the actual DNS records for the domain.
Recursive Resolver: Performs this lookup process for the client and caches the results.
Once you understand this hierarchy, commands like dig . NS, dig com NS, dig google.com NS, and dig google.com stop looking like random commands and start showing you the actual structure behind DNS resolution on the internet.